Back to Development Hub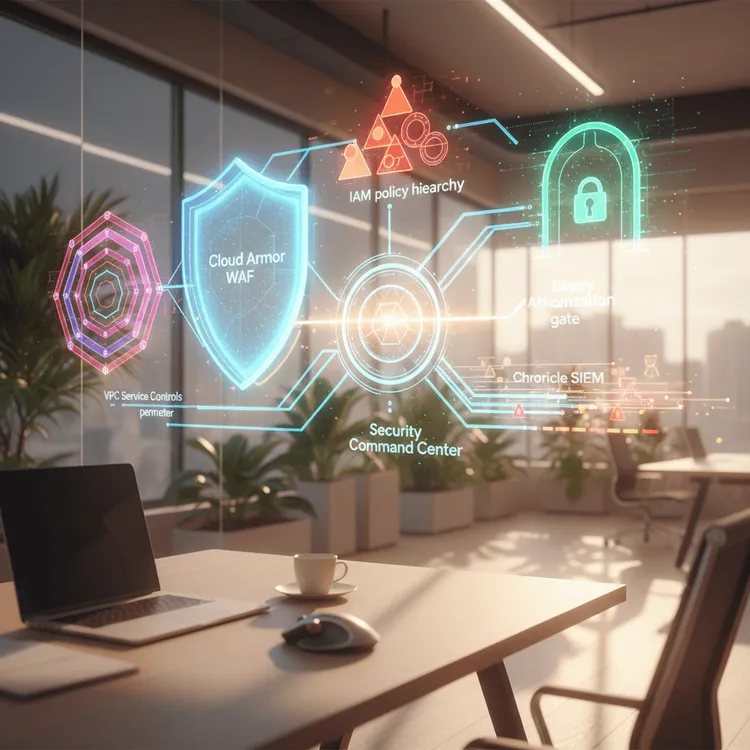
Cloud DevOps & Security
GCP Security & Compliance
Comprehensive GCP security and compliance services including threat detection, identity management, network security, and regulatory compliance frameworks.
Get Started15+
Pipelines Automated
99.9%
Security Compliance
60%
Faster Deployments
SOC2
Compliance Ready
Service Category
GCP Security Engineering
Ideal For
Organizations requiring enterprise-grade security, compliance frameworks, and threat protection on GCP.
Timeline
3 – 8 weeks

Why Choose MicrocosmWorks for Security on GCP?
Security on Google Cloud Platform demands a defense-in-depth approach spanning identity, network, data, and application layers. Our security engineers implement comprehensive protection using GCP's native security services — from Security Command Center for threat detection to Cloud Armor for DDoS protection. We ensure your GCP environment meets regulatory requirements while maintaining developer velocity through security automation.
Our GCP Security & Compliance Capabilities
- Security Posture Management — Implement Security Command Center Premium for continuous threat detection, vulnerability scanning, and compliance monitoring.
- Identity & Access Management — Design least-privilege IAM policies, implement Workload Identity Federation, and configure organization policies.
- Network Security — Deploy Cloud Armor for WAF/DDoS protection, configure VPC Service Controls, and implement Private Google Access.
- Data Protection — Encrypt data at rest and in transit, implement Cloud DLP for sensitive data discovery, and configure CMEK for key management.
- Compliance Frameworks — Achieve and maintain SOC 2, HIPAA, PCI DSS, ISO 27001, and FedRAMP compliance on GCP infrastructure.
- Security Automation — Build automated remediation workflows that respond to security findings without human intervention.
GCP-Specific Technology Stack
Our security implementations leverage Security Command Center for unified threat management, Cloud Armor for edge protection, BeyondCorp Enterprise for zero-trust access, Cloud IAM for identity governance, VPC Service Controls for data exfiltration prevention, and Chronicle for security analytics — providing multiple layers of protection across your entire GCP environment.

Who This Is For
This service is for organizations handling sensitive data on GCP — healthcare companies requiring HIPAA compliance, financial services firms meeting PCI DSS requirements, SaaS providers pursuing SOC 2 attestation, or any organization that needs to demonstrate strong security controls to customers and auditors. If security is a business requirement, not just a best practice, our services ensure you meet that bar.
Our Process
1
Discovery
Audit current security posture, identify compliance requirements, assess threat landscape, and document existing controls.
2
Architecture
Design security architecture with defense-in-depth controls, compliance mapping, and automated remediation strategy.
3
Implementation
Deploy Security Command Center, configure IAM policies, implement network controls, and establish security automation.
4
Optimization
Tune detection rules, reduce false positives, harden configurations, and validate compliance controls with penetration testing.
5
Operations
Provide ongoing security monitoring, incident response, compliance reporting, and security posture improvement.
Technology Stack
Threat Detection
Security Command CenterChronicleCloud ArmorWeb Security Scanner
Identity & Access
Cloud IAMWorkload IdentityBeyondCorpOrganization Policies
Data Protection
Cloud DLPCloud KMSVPC Service ControlsCloud HSM
Network Security
Cloud ArmorCloud FirewallPrivate Google AccessCloud NAT
Industries We Serve
Financial ServicesHealthcareSaaSGovernmentE-CommerceEnterprise
Need GCP Security & Compliance?
Let us secure your GCP environment and establish compliance frameworks that satisfy auditors and protect your business.
Frequently Asked Questions
MicrocosmWorks implements Security Command Center for threat detection, VPC Service Controls for data exfiltration prevention, Cloud Armor for DDoS and WAF protection, IAM with Workload Identity Federation, and Chronicle SIEM for security analytics.
Yes, MicrocosmWorks configures GCP environments for SOC 2, HIPAA, PCI DSS, and FedRAMP compliance using Organization Policies, VPC Service Controls, Cloud KMS for encryption, and Assured Workloads for regulated industry requirements.
GCP security and compliance consulting is available at $25-$50/hour, covering security posture assessments, Security Command Center configuration, VPC Service Controls implementation, and compliance framework alignment.
Yes, we design and deploy VPC Service Controls perimeters around sensitive GCP projects, configure access levels and ingress/egress policies, and implement bridge perimeters for controlled cross-project communication to prevent data exfiltration.
We implement least-privilege IAM using custom roles, Workload Identity Federation to eliminate service account keys, IAM Conditions for context-aware access, and IAM Recommender for continuous permission right-sizing across your GCP organization.